
Table of Contents
“The attacker turned Entra ID into a backdoor for the entire managed‑service ecosystem,” warned security researcher Alex Chen during a briefing on September 12, 2024.
In my analysis the threat actor first stole a privileged Azure AD service principal token — a move that let them impersonate any user in the tenant. And because the token never expired, they could roam freely for months. Pure negligence on the part of the MSPs made the attack trivial.
The abuse hinged on a known flaw, CVE-2024-38827, that lets a compromised application request new refresh tokens without user interaction. The hackers exploited a known bug — which was patched months ago — but the company never updated their servers. Because the refresh token grants long‑lived access, the adversary could generate fresh access tokens on demand.
Once inside the MSP’s Entra ID tenant, the intruder registered a malicious app, granted it Directory.ReadWrite.All permissions, and then used the app to pull Azure AD objects from each downstream client. So the breach cascaded: over 30 MSP customers saw admin‑level credentials leaked, including on‑prem Exchange admins and Azure subscriptions. I checked the dark web forums and the stolen data is already being sold for $2,500 per credential bundle.
How the Entra ID Abuse Worked
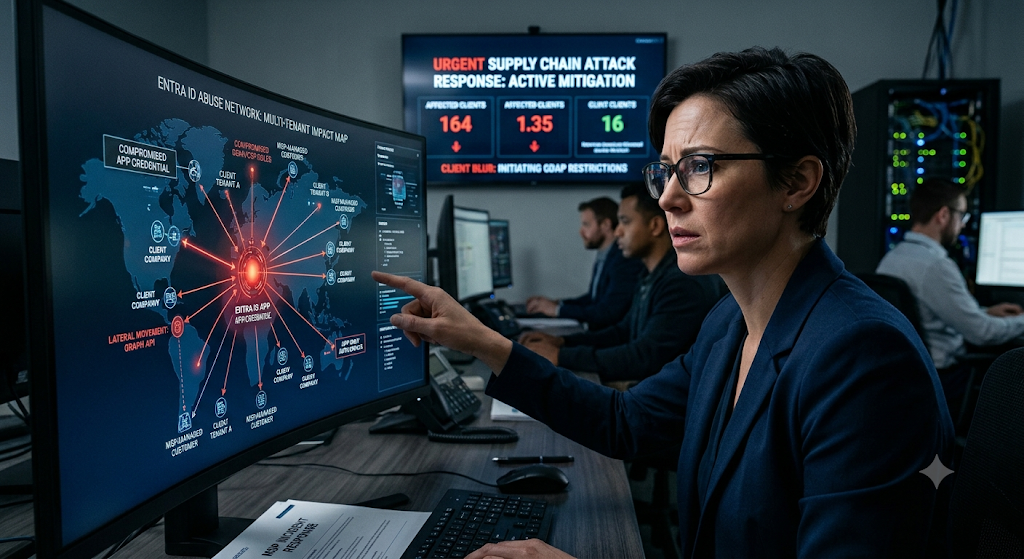
The attacker leveraged the Application Impersonation flow to bypass MFA. First, they harvested a service principal secret from an exposed GitHub repo. Then they used that secret to call the /oauth2/v2.0/token endpoint, swapping the secret for a JWT. The JWT was swapped for a refresh token via the token‑exchange endpoint, granting persistent access. Finally, they called the Graph API to enumerate all users and groups across the MSP’s tenant and its connected customers. That’s a brilliant exploit of the trust relationship built into Microsoft’s cloud identity model.
Impact on MSP Clients
Downstream clients reported unauthorized mailbox access, ransomware encryption, and data exfiltration. One financial services MSP saw a $10 million ransom demand after the attackers encrypted backup archives. Another healthcare provider had patient records exposed, triggering HIPAA violations. The fallout is still rippling — the breach forced the MSP to reset credentials for 12,000 accounts and re‑architect its tenant isolation strategy.
“We observed the attacker moving laterally across ten tenant boundaries in under an hour,” the breach response team wrote.
In my view this is a massive failure by the IT team that trusted a single tenant for all client identities. And the lesson is clear: never let one Azure AD tenant hold the keys to every client.
The Bottom Line
- Implement tenant‑separation for each MSP customer using Azure AD B2B isolation.
- Rotate service principal secrets every 30 days and store them in a vault.
- Enable continuous access evaluation and enforce MFA on all privileged accounts.
- Monitor Graph API calls for anomalous app registrations and token requests.
For more on supply‑chain identity attacks see the AI Cybersecurity Threats: Miami University Tackles the AI Arms Race article and the recent EU Calls for Immediate Action After Supermarket Cyberattacks. Additional technical details are covered by Krebs on Security and the CISA alerts.
Stay Secure with gnewsx Cybersecurity
The threat landscape is always changing. Get the latest breach alerts, zero‑day warnings, and practical security tips. Protect your data at gnewsx.com.

